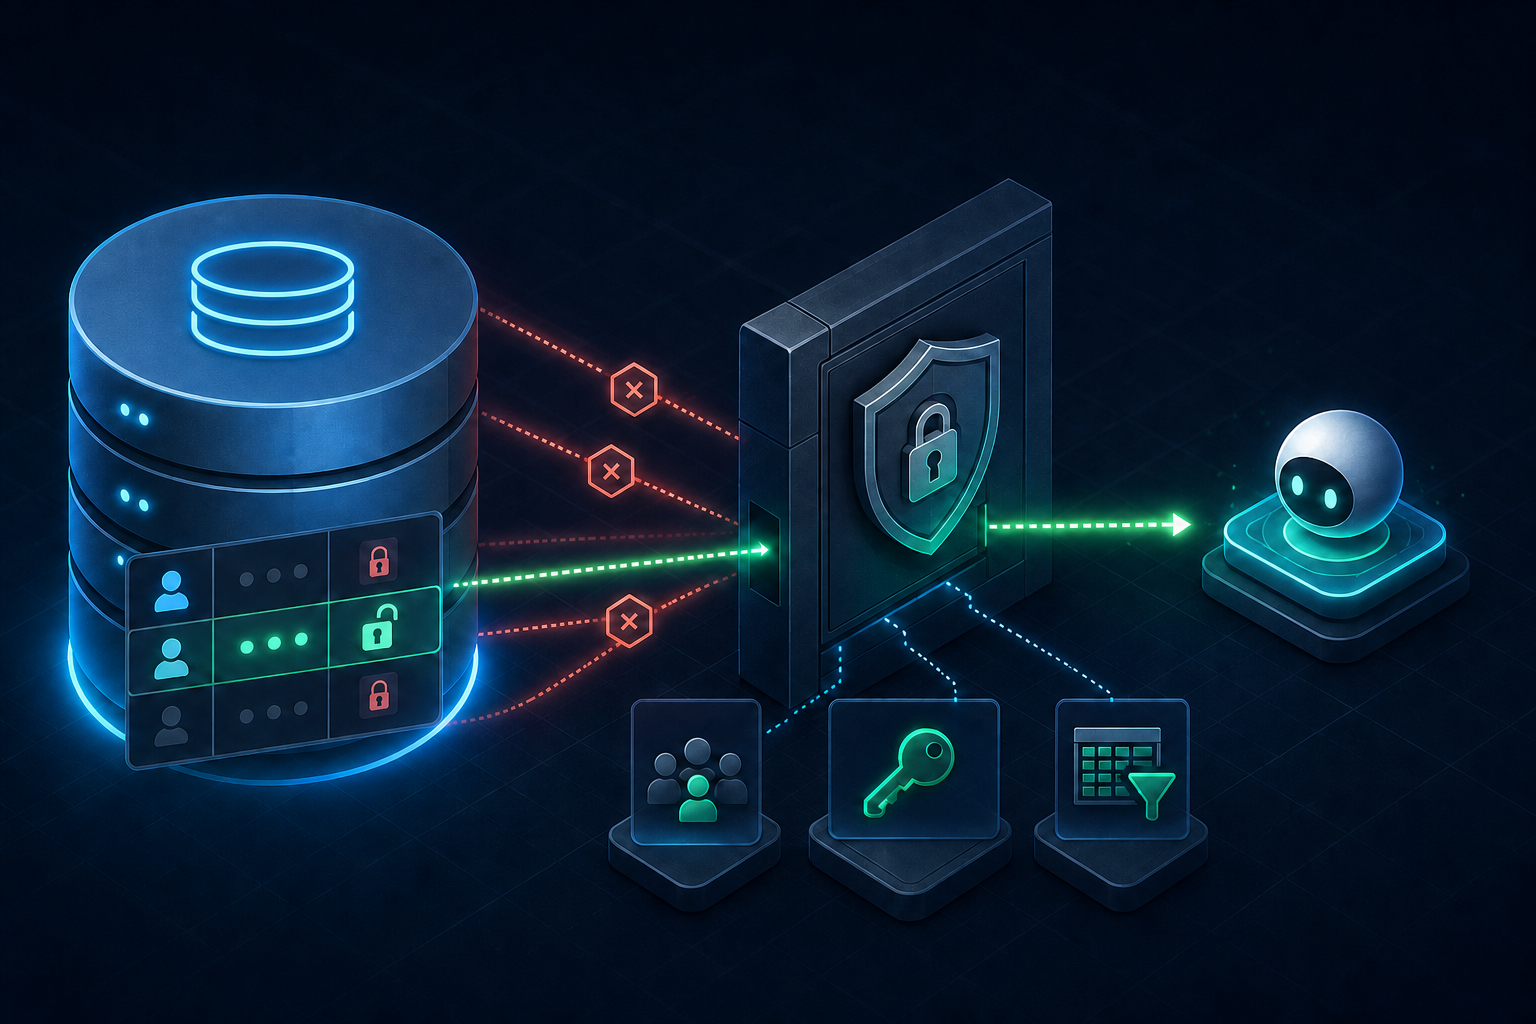
How to Create a Least-Privilege PostgreSQL Role for AI Agents
A production-ready PostgreSQL access model for AI agents using restricted role attributes, precise grants, Row Level Security, session limits, and negative permission tests.
Read guideTested solutions, reproducible failure modes, and practical verification steps for modern web development.
A production-ready PostgreSQL access model for AI agents using restricted role attributes, precise grants, Row Level Security, session limits, and negative permission tests.
Read guide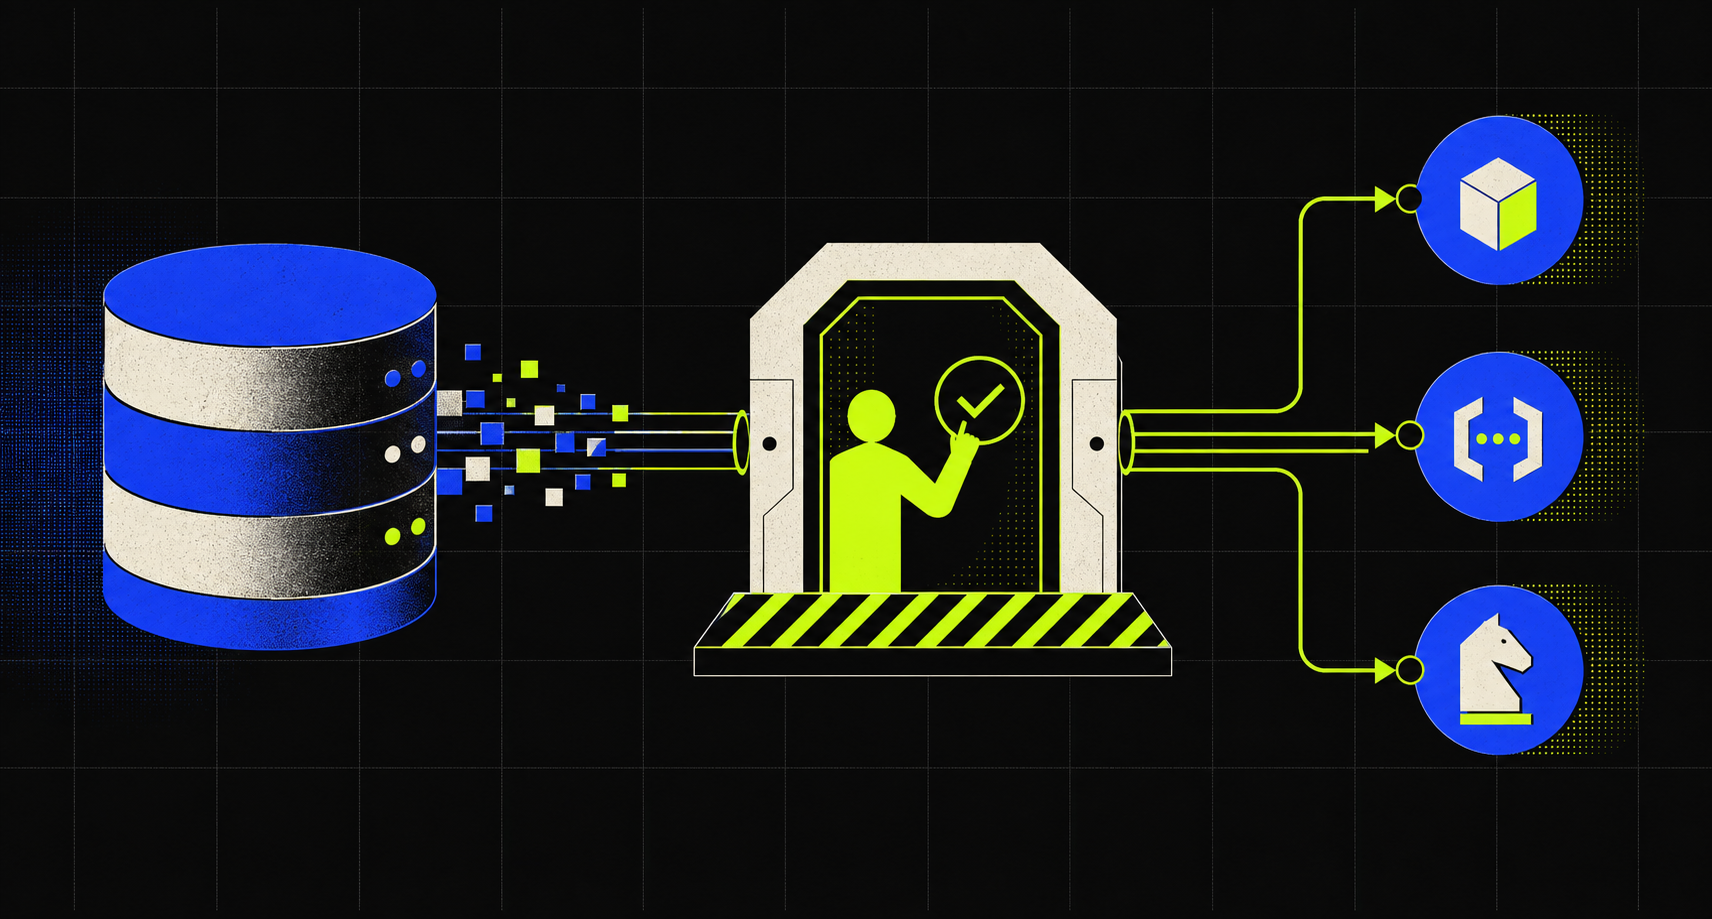
A practical architecture for turning a reviewed PostgreSQL schema into typed MCP tools with least-privilege roles, strict inputs, bounded queries, and human approval.
Read guide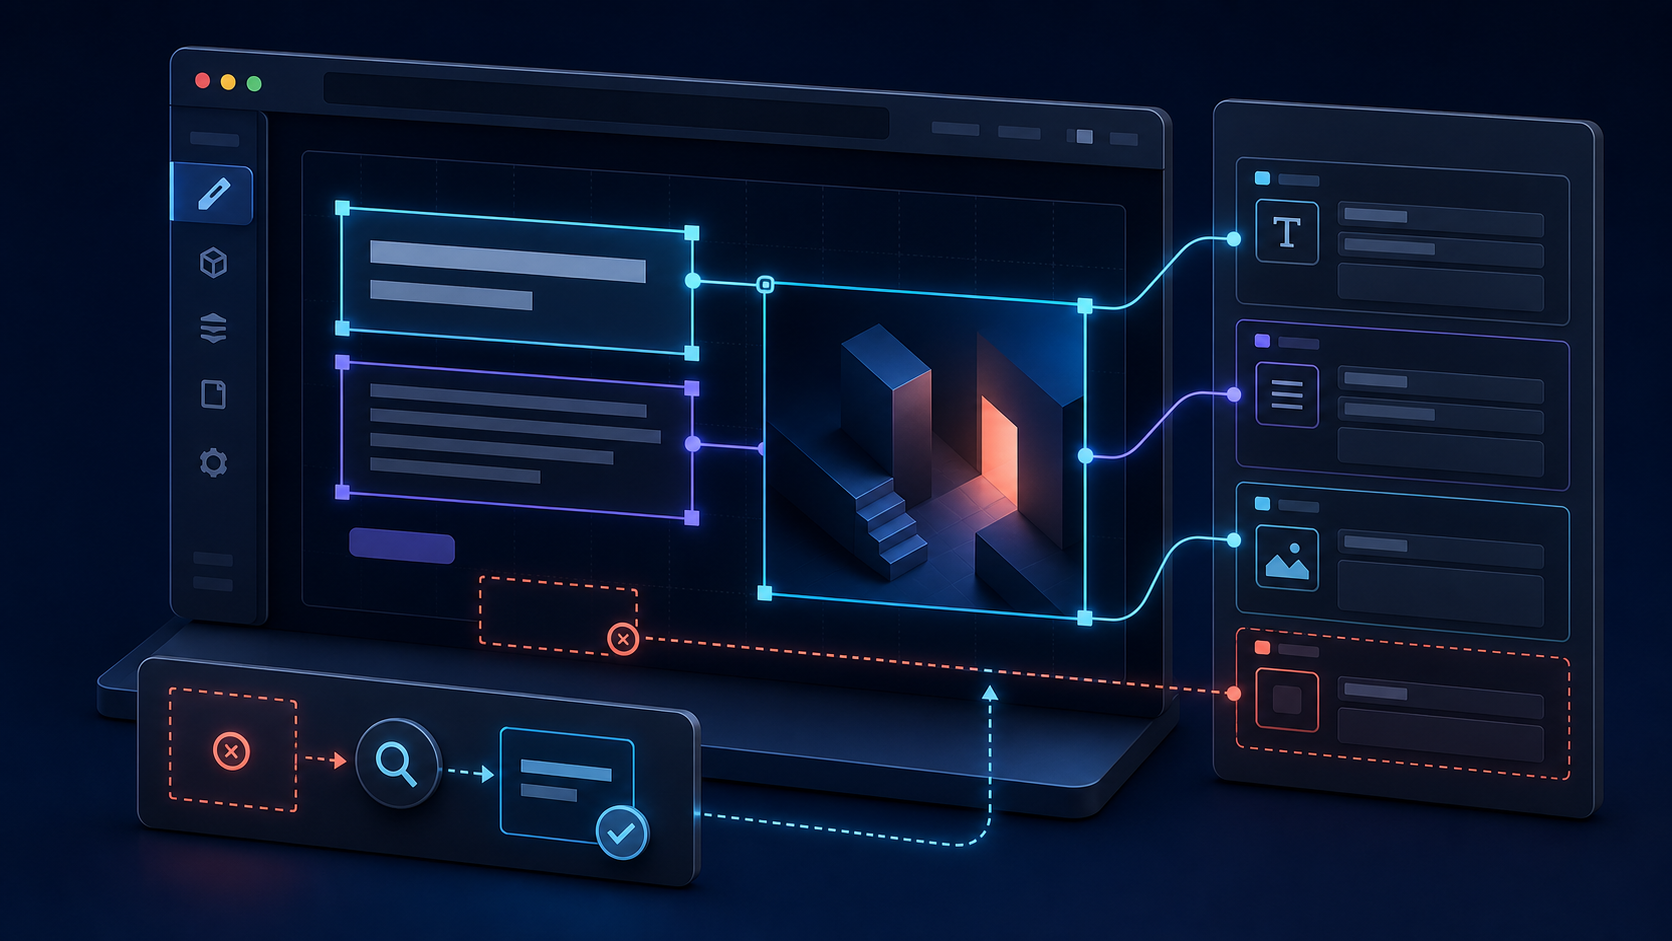
A layer-by-layer debugging guide for missing overlays, broken click-to-edit links, incorrect field paths, stega leaks, iframe failures, and live updates in Next.js App Router.
Read guide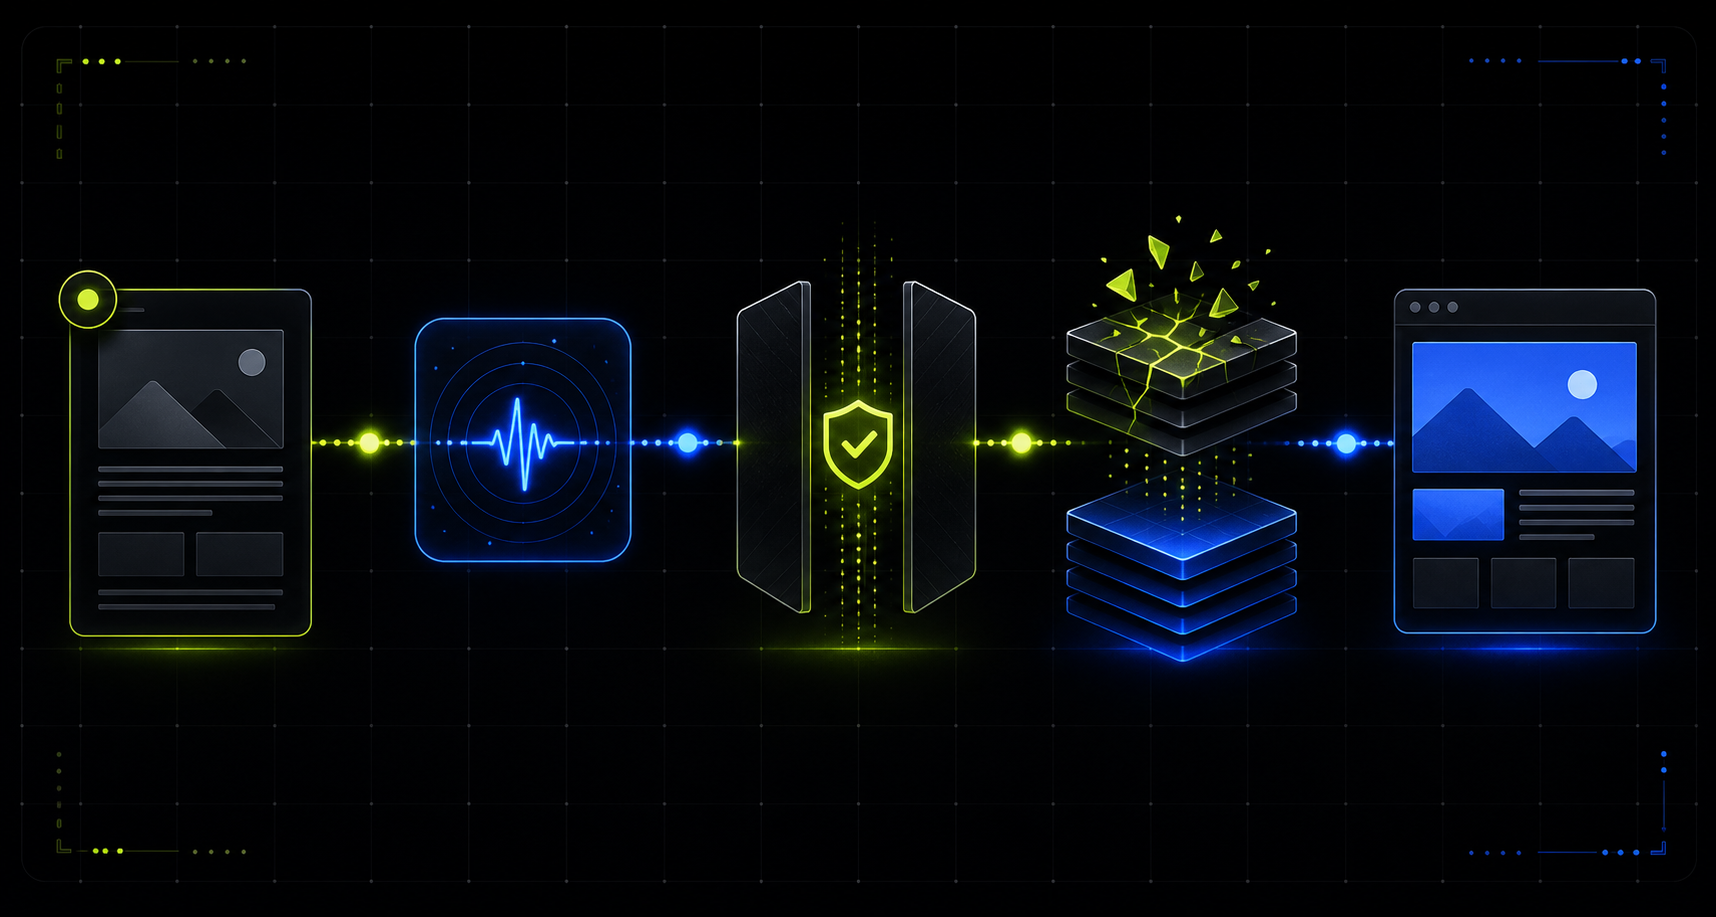
A practical checklist for tracing stale Sanity content through GROQ, the API CDN, Next.js caching, signed webhooks, cache tags, and production on Vercel.
Read guide
A source-to-browser debugging guide for Draft Mode activation, cookies, draft perspectives, tokens, CORS, stega, and live preview in the Next.js App Router.
Read guide
A systematic guide to finding stale content across drafts, perspectives, the Sanity CDN, Next.js caches, and revalidation—without guessing which cache to clear.
Read guide